As organizations increasingly deploy AI models in production environments, concerns around security, compliance, and accountability are growing just as fast. Ensuring that only authorized users can access sensitive AI systems—and being able to track every interaction—is essential for maintaining trust and transparency. This is where Carlo PEaaS (Policy Enforcement as a Service) comes in, offering a powerful solution for role-based access and AI audit trails.
The Challenge of Securing AI
AI systems often process sensitive data, make critical decisions, and operate at high speed across distributed infrastructure. Without proper access governance and traceability, organizations risk unauthorized use, model misuse, or regulatory non-compliance. Traditional security approaches often fall short when applied to dynamic AI environments, where data flows and decision paths are not always predictable.
Carlo Security: A Modern Approach
Carlo PEaaS is designed to solve these modern challenges with a security-first architecture tailored for AI and ML workflows. Built with compliance, privacy, and operational integrity in mind, Carlo security integrates seamlessly with popular AI platforms and orchestrates fine-grained access control policies across AI pipelines.
Role-Based Access Control (RBAC)
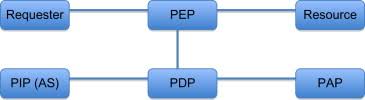
At the heart of Carlo PEaaS is its role-based access control (RBAC) system. This allows organizations to define precise user roles (e.g., Data Scientist, ML Engineer, Compliance Officer) and assign permissions based on these roles. Only authorized users can train models, view datasets, deploy inference endpoints, or access model outputs—helping to enforce access control AI best practices.
AI Audit Trails for Full Transparency
Carlo also automatically generates AI audit trails, logging every interaction with an AI model or data source. Whether a user is querying a model, updating a pipeline, or changing configuration parameters, Carlo records the event with detailed metadata—who did what, when, and from where.
These AI audit trails are essential for:
Regulatory compliance (e.g., GDPR, HIPAA, SOC 2)
Internal audits and forensic investigations
Proving model integrity and lineage
By offering immutable logs and tamper-proof audit records, Carlo helps build accountability and trust across AI stakeholders.
Enabling Secure AI Compliance
Regulations are catching up to AI, with laws increasingly mandating transparency, data protection, and explainability. Carlo PEaaS enables secure AI compliance by ensuring that every action in the AI lifecycle is authorized, tracked, and reviewable. Carlo’s built-in compliance tools help teams meet regulatory demands without slowing down development or deployment.
Why Carlo PEaaS Is Different
Unlike generic access control platforms, Carlo is purpose-built for AI:
It understands ML concepts like training jobs, inference endpoints, and feature stores.
It integrates with tools like Kubernetes, TensorFlow, PyTorch, and Airflow.
It supports dynamic policy enforcement that adapts to model lifecycle stages.
These capabilities make Carlo a key enabler of access control AI that scales with your organization’s growth and complexity.
Final Thoughts
With AI becoming a core part of enterprise infrastructure, securing its use is no longer optional. Carlo PEaaS provides a robust foundation for role-based permissions, AI audit trails, and secure AI compliance. By embedding Carlo security into your AI stack, you not only reduce risk—you build a future-ready framework for ethical, auditable AI operations.